Conference papers

Learning Transferable Representations from Operating System Entities via Provenance Graph Distillation featured image

Learning Transferable Representations from Operating System Entities via Provenance Graph Distillation

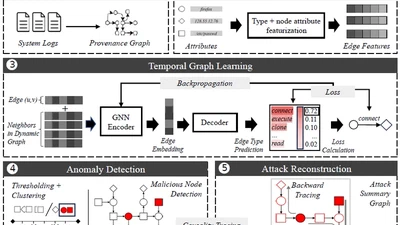
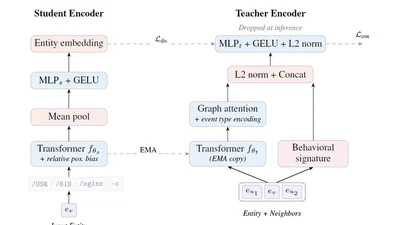
Provenance graphs capture causal interactions among operating-system entities, underpinning modern endpoint intrusion detection. Existing graph-based detectors use generic text …

t-bilot
•
LARES: Host-centered Lateral Movement Detection via Inductive Graph Reasoning featured image

LARES: Host-centered Lateral Movement Detection via Inductive Graph Reasoning

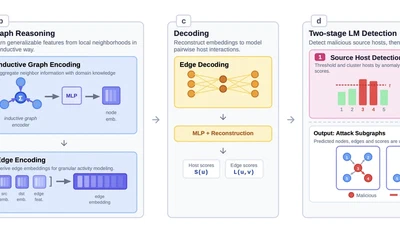
Detecting lateral movement (LM) within enterprise networks remains a difficult challenge, with existing state-of-the-art methods often failing to identify such activity …

t-bilot
•
PIDSMaker: Building and Evaluating Provenance-based Intrusion Detection Systems featured image

PIDSMaker: Building and Evaluating Provenance-based Intrusion Detection Systems

Recent provenance-based intrusion detection systems (PIDSs) have demonstrated strong potential for detecting advanced persistent threats (APTs) by applying machine learning to …

t-bilot
•
Inside Out: A Paradigm Shift In VM Introspection featured image

Inside Out: A Paradigm Shift In VM Introspection

We present GoodKit, a new framework for live virtual machine introspection (LVMI) designed for performance, scalability, and safe integration in modern cloud environments. Unlike …

d-teguia
•
Work-in-Progress: RegTrack: Uncovering Global Disparities in Third-party Advertising and Tracking featured image

Work-in-Progress: RegTrack: Uncovering Global Disparities in Third-party Advertising and Tracking

Third-party advertising and tracking (A&T) are pervasive across the web, yet user exposure varies significantly with browser choice, browsing location, and hosting jurisdiction. We …

t-prasad
•
Sometimes Simpler is Better: A Comprehensive Analysis of State-of-the-Art Provenance-Based Intrusion Detection Systems featured image

Sometimes Simpler is Better: A Comprehensive Analysis of State-of-the-Art Provenance-Based Intrusion Detection Systems

Provenance-based intrusion detection systems (PIDSs) have garnered significant attention from the research community over the past decade. Although recent studies report near …

t-bilot
•
ORTHRUS: Achieving High Quality of Attribution in Provenance-based Intrusion Detection Systems featured image

ORTHRUS: Achieving High Quality of Attribution in Provenance-based Intrusion Detection Systems

Past success in applying machine learning to data provenance graphs -- a structured representation of the history of operating system activities -- to detect host system intrusions …

b-jiang
•

On the Reproducibility of Provenance-based Intrusion Detection that uses Deep Learning

As cyber-threats grow in scale and sophistication, intrusion detection systems that incorporate system provenance and deep learning have emerged as a promising direction for …

t-abrar
•
SafeBPF: Hardware-assisted Defense-in-depth for eBPF Kernel Extensions featured image

SafeBPF: Hardware-assisted Defense-in-depth for eBPF Kernel Extensions

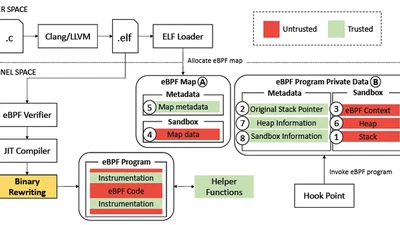
The eBPF framework enables execution of user-provided code in the Linux kernel. In the last few years, a large ecosystem of cloud services has leveraged eBPF to enhance container …

sy-lim
•
FetchBPF: Customizable Prefetching Policies in Linux with eBPF featured image

FetchBPF: Customizable Prefetching Policies in Linux with eBPF

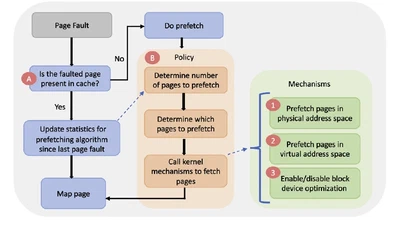
Monolithic operating systems are infamously complex. Linux in particular has a tendency to intermingle policy and mechanisms in a manner that hinders modularity. This is especially …

x-cao
•